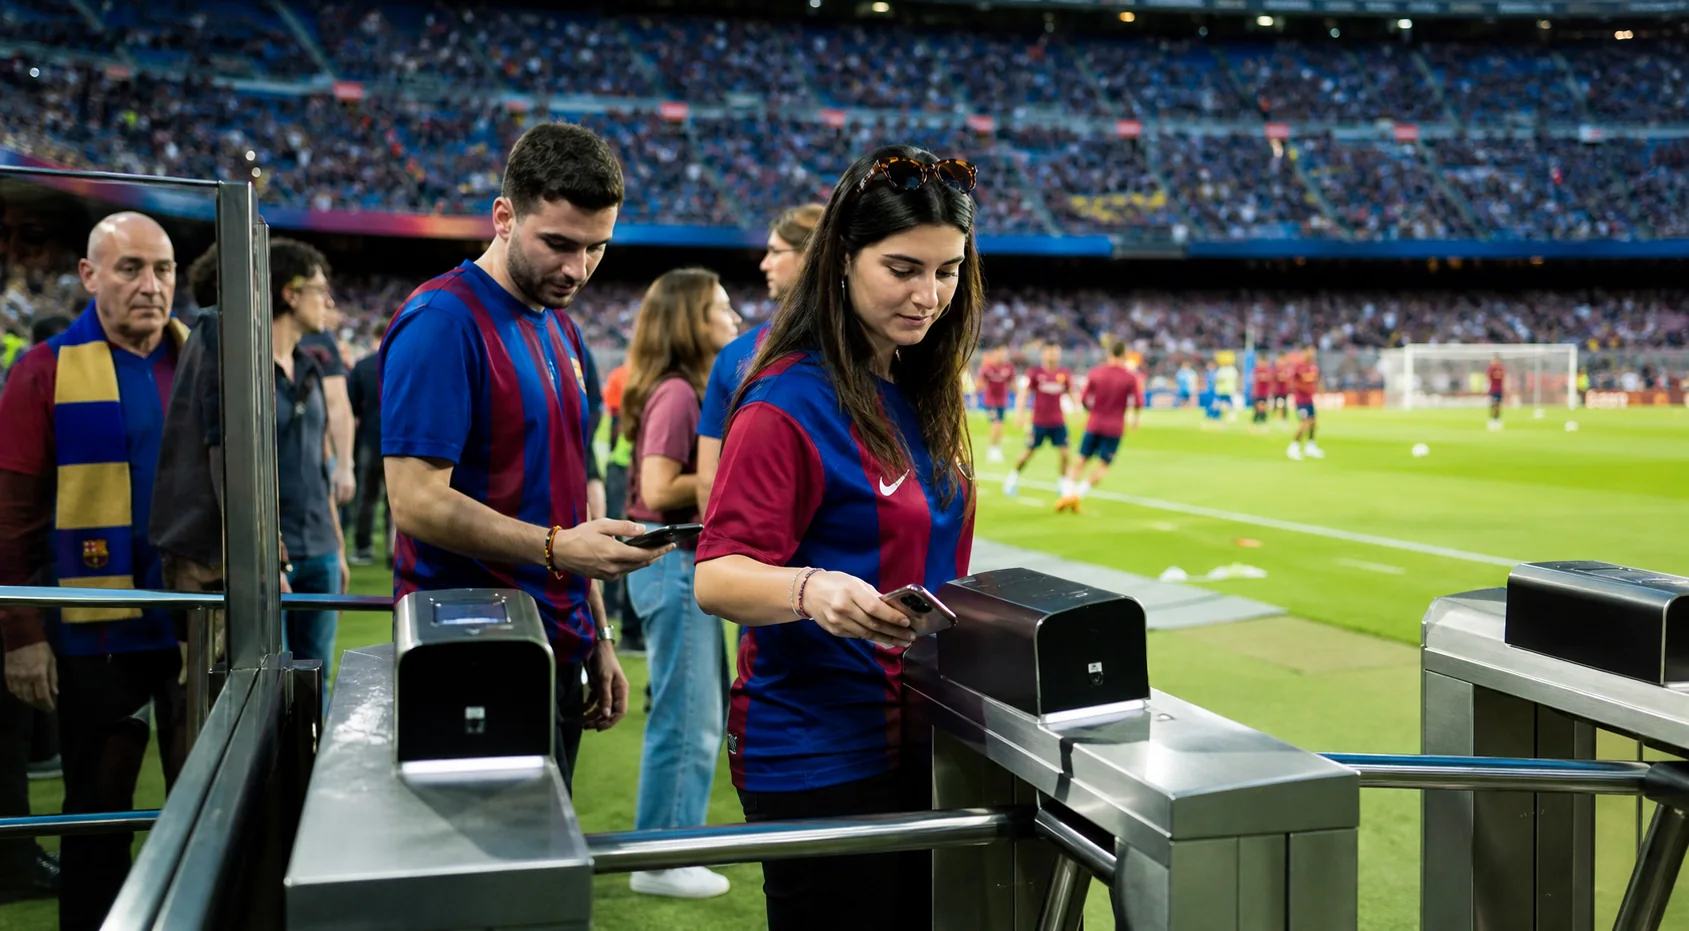
Ticketing is often treated as a commerce stack until a gate fails or a transfer is disputed. In reality it is an access-control system with a customer relationship attached. The first decision is the verification objective: prevent duplicate entry, validate entitlement, manage a restricted zone, or establish a persistent account. Each objective warrants a different amount of data and friction. The intended result should be stated in plain operational language before specifications are written. The venue should make this choice deliberately rather than inheriting it from a default setting. It is a decision about people, process, and physical space as much as a decision about equipment.
A useful design separates ticket possession from identity proof. A rotating barcode may be sufficient for ordinary entry, while credential checks can be reserved for staff, working areas, age-controlled spaces, or a specific safety requirement. This reduces unnecessary collection and avoids turning an occasional spectator journey into a complex enrolment process. A clear readiness check exposes dependencies that procurement documents often miss. Frontline staff need a short instruction that remains usable when communication is imperfect. Document the normal workflow and the exception workflow; both need an owner. That discipline keeps investment choices connected to a credible event-day workflow.
Build a clear exception path before launch. Phones lose charge, screens break, connectivity drops, families arrive with tickets in one device, and a legitimate transfer may look unusual to a scanner. Stewards need a limited tool, documented authority, and a way to record the decision without exposing a full customer profile in public view. Observe the boundary between teams, where handoffs and unclear language commonly cause delay. Prefer a small intervention made early to a dramatic change made after options have narrowed. Field checks should challenge the model whenever the live environment has changed.
Fraud controls work best when they are layered. Short-lived credentials, transfer rules, secure account recovery, anomaly review, and gate-side duplicate detection can each address a different failure. Overreacting to a suspicious pattern by blocking an entire group creates operational and reputational risk, so high-impact decisions should have human review and an appeal route. Pair every speed or utilisation metric with an observation of fairness, access, or resilience. Use evidence with humility: sensors, records, and observations each describe only part of the scene. Protect the route for people who need more time, space, or assistance to act on the instruction.
Measure the whole entry outcome, not only scan speed. Review successful first-pass scans, exception rate, manual overrides, re-entry disputes, assistance-lane wait, and false rejection reports. Break results down by gate and time window. A low average scan time can conceal a badly designed accessibility route or an exception queue that staff are quietly absorbing. Privacy and safety rules need a named custodian and a route for frontline questions. Access should be proportionate to the task, with logs that support review without creating busywork. Limit collection and visibility of personal information to what the task genuinely requires.
Privacy governance should specify purpose, retention, access roles, and the link between ticket data and any other records. Do not make gate staff arbiters of data disputes. Give customers a simple support channel, give supervisors a proportionate view of the issue, and log administrative lookups so the venue can audit whether sensitive information was accessed appropriately. Temporary event changes should have a deadline, inspection, and rollback plan. An exercise should include at least one failed assumption, so recovery is genuinely practised. Rehearse the degraded mode before a crowded event makes experimentation unsafe.
Roll out capability in stages. Start with a clear ticket format and reliable standard entry, then add restricted access or account features only where a tested need exists. Publish event-day instructions in accessible formats, rehearse offline validation, and preserve a manual reconciliation process. A smooth entry system is one that continues to make defensible decisions when the ideal digital journey is unavailable. Learning compounds when the team changes one variable at a time and records the outcome. The mature outcome is a service the venue can explain, operate, and improve with confidence.